Enterprise Information & Technology
Cyber Resilience
Reference Content ID: #LEAD-ES50046ALL
Introduction to Cyber Resilience
Cyber Resilience is an organisation’s ability to anticipate, withstand, respond to, and recover from cyber disruption while maintaining essential operations. It combines preparedness, protection, adaptability, and recovery.
Its core principles focus on understanding cyber risks, protecting critical assets, maintaining operational continuity, and improving response capabilities.
Key focus areas include governance, cybersecurity, technology resilience, data protection, incident response, business continuity, workforce readiness, and continuous improvement.
Cyber Resilience applies across industries, functions, and operating models. It supports on-site, hybrid, and remote teams by sustaining productivity, strengthening collaboration, supporting employee well-being, and enabling dependable digital workflows.
Applied consistently, Cyber Resilience strengthens organisational confidence, continuity, and adaptability. It helps enterprises protect value while operating effectively through cyber disruption.
Definition and Scope
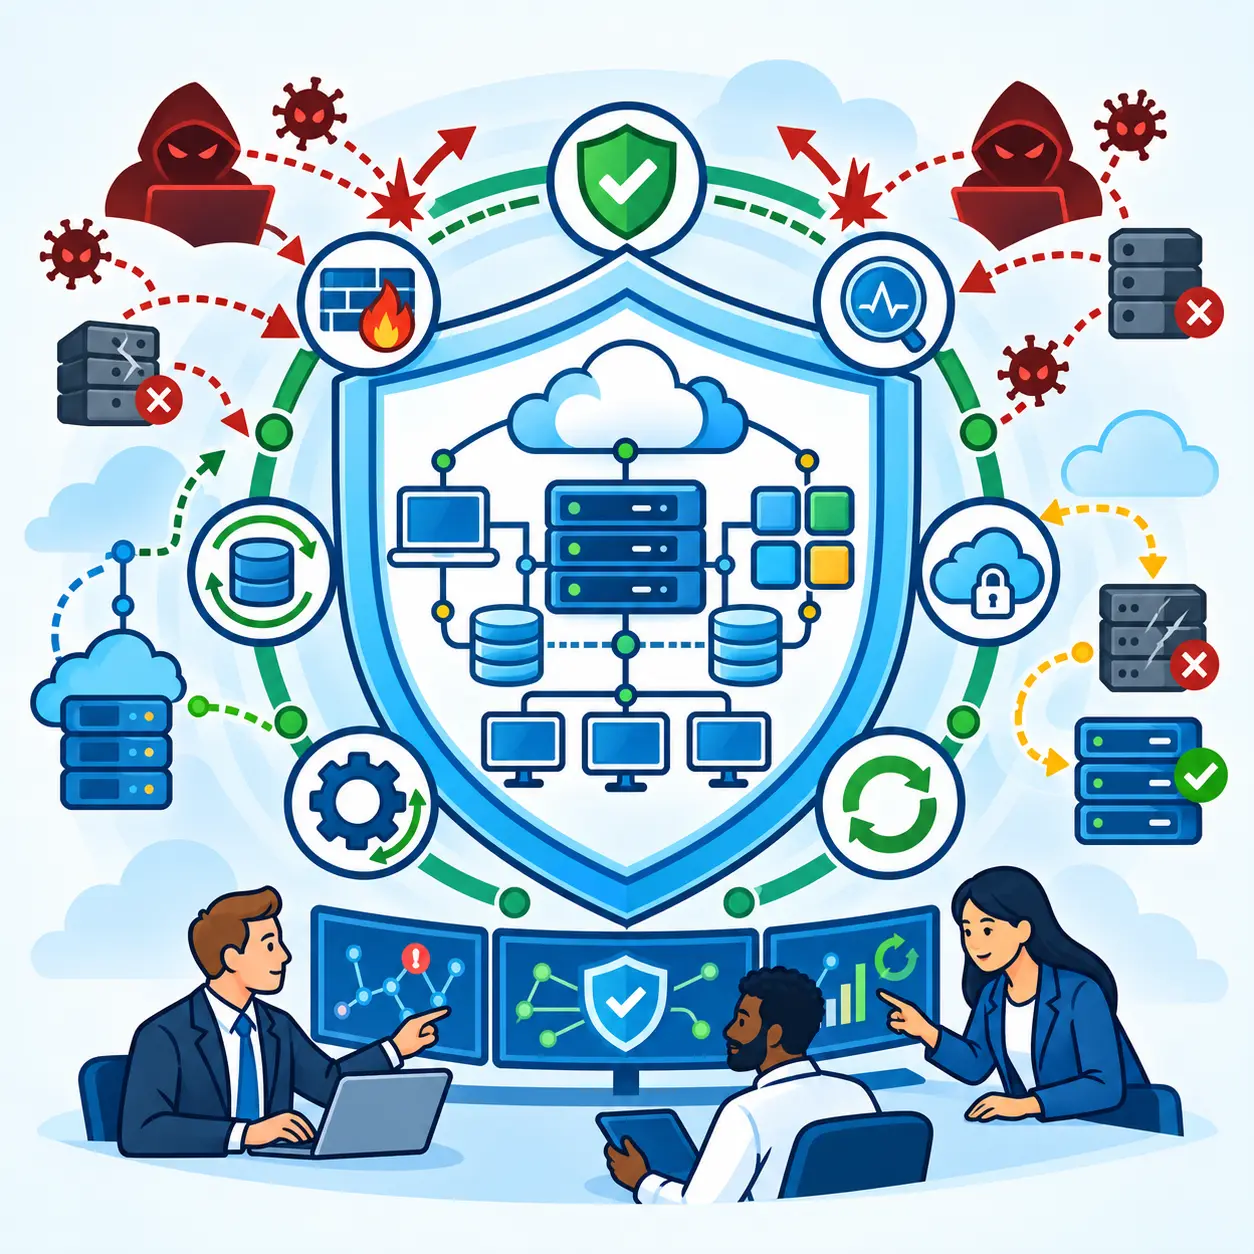
Cyber Resilience defines how an organisation prepares for, withstands, responds to, and recovers from cyber disruption while sustaining critical operations. Its scope extends beyond cybersecurity by combining protection with continuity, adaptability, and recovery capabilities.
It includes governance, cyber risk management, security controls, technology and data resilience, incident response, business continuity, recovery planning, and workforce preparedness. These domains interact across business processes, applications, infrastructure, suppliers, and digital services to reduce disruption and support coordinated recovery.
Activities unrelated to cyber-enabled disruption or the resilience of digital operations generally fall outside its scope.
Cyber Resilience therefore connects preventive, responsive, and recovery capabilities. Together, they enable organisations to maintain essential services and adapt effectively when cyber incidents occur.
Why Digital Sovereignty Matters
Cyber Resilience matters because organisations depend on digital services that must remain dependable despite cyber disruption. It supports strategic continuity, trusted operations, and informed risk decisions.
It helps organisations respond to evolving threats, technology change, regulatory pressures, and digital interdependence while protecting critical services and maintaining performance.
Executives value risk visibility and continuity; managers benefit from coordinated response and recovery; end users gain reliable access to essential systems and services.
- Executive Decisions: Improves visibility of cyber risk and resilience priorities.
- Operational Efficiency: Reduces disruption through coordinated preparation and recovery.
- Innovation Confidence: Enables digital change with resilience safeguards.
Cyber Resilience strengthens confidence, adaptability, and operational stability. It helps organisations pursue strategic goals while remaining prepared for cyber disruption.
Business Case and Strategic Justification
Cyber Resilience is a strategic investment that protects business value by strengthening the organisation’s ability to continue operating through cyber disruption. It aligns resilience priorities with corporate objectives, risk appetite, regulatory expectations, and digital transformation.
Investment is justified through reduced disruption costs, faster recovery, improved operational efficiency, stronger customer confidence, and lower exposure to financial and reputational loss. Relevant measures include recovery time, incident frequency, service availability, control effectiveness, and estimated loss avoidance.
Typical benefits include:
- Business Continuity: Sustains critical operations during cyber incidents.
- Risk Reduction: Limits operational, financial, and reputational exposure.
- Faster Recovery: Improves response coordination and restoration times.
- Stakeholder Confidence: Strengthens trust among customers, partners, and leadership.
- Digital Enablement: Supports innovation and transformation with greater resilience.
Cyber Resilience strengthens strategic preparedness while improving operational confidence. Organisations should prioritise investments according to critical services, material risks, and measurable resilience objectives.
DON’T REINVENT THE WHEEL!
Get access to our Enterprise Standards to Drive Performance, Minimise Cost and Maximise Value.
How is Cyber Resilience Used?
Cyber Resilience is applied through a structured framework that combines implementation stages, awareness of common weaknesses, and proven practices. Together, these perspectives help organisations build, operate, and improve resilient capabilities.
Key Phases and Process Steps define the sequence for assessing risks, strengthening controls, preparing responses, and supporting recovery. Identifying Pitfalls and Challenges highlights antipatterns and poor practices that can weaken resilience. Learning from Outperformers examines best and leading practices that improve preparedness, adaptability, and performance.
These perspectives work together to provide a balanced approach to Cyber Resilience. They help organisations implement appropriate measures, avoid recurring weaknesses, and continuously improve their ability to withstand and recover from cyber disruption.
Key Phases and Process Steps
Cyber Resilience follows a structured lifecycle that connects preparation, protection, response, recovery, and improvement. The ten steps provide a practical sequence for managing resilience across business and technology environments:
1. Assess Context
Identify critical services, dependencies, threats, and business priorities.
2. Define Governance
Establish ownership, accountability, policies, and decision rights.
3. Analyse Risk
Evaluate cyber threats, vulnerabilities, impacts, and resilience gaps.
4. Protect Assets
Apply controls to safeguard systems, data, and infrastructure.
5. Prepare Continuity
Develop response, continuity, and recovery arrangements.
6. Detect Disruption
Monitor for incidents, anomalies, and emerging threats.
7. Respond Rapidly
Contain incidents and coordinate operational actions.
8. Recover Services
Restore critical systems and business capabilities.
9. Validate Readiness
Test plans, controls, and recovery procedures regularly.
10. Improve Continuously
Apply lessons learned and strengthen resilience capabilities.
Together, these phases create an end-to-end resilience cycle. They help organisations reduce disruption, accelerate recovery, and improve preparedness over time.
Identifying Pitfalls and Challenges: Antipatterns and Worst Practices
Cyber Resilience can be weakened by recurring design flaws and poor operational behaviours. Recognising these patterns helps organisations avoid preventable gaps.
5 Antipattern Examples:
5 Worst Practice Examples:
Avoiding these weaknesses strengthens preparedness, coordination, and recovery capability.
Learning from Outperformers: Best Practices and Leading Practices
Outperforming organisations combine disciplined fundamentals with advanced resilience capabilities. Their practices strengthen preparedness, adaptability, and recovery performance.
5 Best Practice Examples:
5 Leading Practice Examples:
Together, these practices improve readiness, response, and long-term resilience maturity.
Who is Typically Involved with Cyber Resilience?
Cyber Resilience depends on coordinated participation across leadership, management, technical teams, and users. Clear responsibilities enable faster decisions, effective execution, and accountable oversight.
Typical roles include:
- Executive Sponsor: Sets direction, priorities, and funding.
- Resilience Lead: Coordinates planning, implementation, and improvement.
- Security Lead: Manages threats, controls, detection, and response.
- Operations Manager: Maintains critical services and recovery readiness.
- Technology Owner: Ensures resilient systems, infrastructure, and dependencies.
Stakeholder impacts include:
- Executives: Gain clearer risk and investment visibility.
- Managers: Coordinate continuity and recovery activities.
- End Users: Support secure behaviours and dependable operations.
Defined roles strengthen collaboration and accountability. Together, participants improve preparedness, response, and recovery outcomes.
Where is Cyber Resilience Applied?
Cyber Resilience applies wherever digital systems, data, and connected services support critical business activities. Its relevance spans both operational and customer-facing environments.
Primary domains include:
- Information Technology: Protects systems, infrastructure, and digital services.
- Operations: Maintains essential processes during cyber disruption.
- Finance: Safeguards transactions, records, and financial continuity.
- Customer Service: Supports reliable access to customer-facing platforms.
- Supply Chain: Strengthens resilience across suppliers and digital dependencies.
Illustrative scenarios include:
- Remote Operations: Teams maintain secure access during a cyber incident.
- Service Recovery: IT restores critical applications after disruption.
Cyber Resilience is therefore applicable across functions and operating models. Its coordinated use helps organisations sustain critical services and recover effectively.
When Should You Embrace Cyber Resilience?
Cyber Resilience should be adopted when digital dependency, operational exposure, or organisational change increases potential disruption. Effective timing ensures resilience is built before risks become critical.
Key adoption signals include:
- Digital Transformation: New technologies increase dependency and cyber exposure.
- Business Growth: Expansion creates additional systems, users, and risks.
- Technology Refresh: Modernisation provides opportunities to embed resilience.
- Rising Threats: Increased cyber activity requires stronger preparedness.
- Regulatory Change: New obligations demand improved resilience and accountability.
Prerequisites are:
- Stakeholder Alignment: Ensure shared commitment across leadership and key functions.
- Clear Ownership: Define accountability for Cyber Resilience activities.
- Resource Availability: Provide sufficient people, budget, and technology.
- Risk Visibility: Understand critical threats, vulnerabilities, and dependencies.
- Security Maturity: Maintain established cybersecurity controls and practices.
- Continuity Readiness: Have business continuity and recovery capabilities in place.
- Incident Management: Ensure effective processes for detecting, responding to, and managing incidents.
Recognising these signals supports timely adoption. Strong prerequisites help organisations implement Cyber Resilience consistently and sustainably.
Most Common Cyber Resilience Artefacts
Cyber Resilience artefacts provide structured guidance for assessing risks, preparing responses, maintaining operations, and recovering from disruption. They support consistent execution, accountability, and informed decision-making.
The most common artefacts include:
- Cyber Resilience Strategy: Defines objectives, priorities, governance, and overall resilience direction.
- Cyber Risk Assessment: Identifies threats, vulnerabilities, impacts, and critical dependencies.
- Incident Response Plan: Guides coordinated actions for detecting, containing, and managing incidents.
- Business Continuity Plan: Defines how critical business activities continue during disruption.
- Cyber Recovery Plan: Documents procedures for restoring systems, data, and digital services.
Together, these artefacts connect prevention, response, continuity, and recovery. They strengthen preparedness, clarify responsibilities, and support continuous improvement.
The Artefacts Table
The table below summarises five common Cyber Resilience artefacts and their practical application. Together, they support structured planning, response, continuity, and recovery.
| Artefact | Description | Practical use |
|---|---|---|
| Cyber Resilience Strategy | Defines resilience objectives, priorities, and governance. | Guides investment and improvement decisions. |
| Cyber Risk Assessment | Identifies threats, vulnerabilities, impacts, and dependencies. | Prioritises resilience actions. |
| Incident Response Plan | Defines coordinated incident management procedures. | Guides containment and response. |
| Business Continuity Plan | Defines arrangements for maintaining critical activities. | Supports operations during disruption. |
| Cyber Recovery Plan | Defines restoration procedures. | Restores systems, data, and services. |
These artefacts provide complementary guidance throughout the resilience lifecycle. Their consistent use strengthens preparedness, coordination, and recovery capability.